CASE STUDY
ÉTUDE DE CAS
How StampRise built a multi-framework compliance infrastructure in three days
"If you are a lean team selling to enterprises, compliance is not a cost center. It is the thing that lets you compete with companies twenty times your size."
TL;DR
- Challenge: StampRise, a founder-led event tech startup, needed SOC 2, ISO 27001, and GDPR simultaneously and across seven regions, but the startup didn’t have a security team and a previous, manual attempt failed after three months of trying.
- Solution: StampRise used Vanta to unify all three frameworks under a single control set and automate evidence collection, all made practical by native integrations to StampRise's existing stack.
- ROI: StampRise became audit-ready in three days, saving approximately 300 hours and a GRC hire, and built a compliance posture that commands higher prices in enterprise deals.
The company
StampRise brings gamification to live events at a global scale
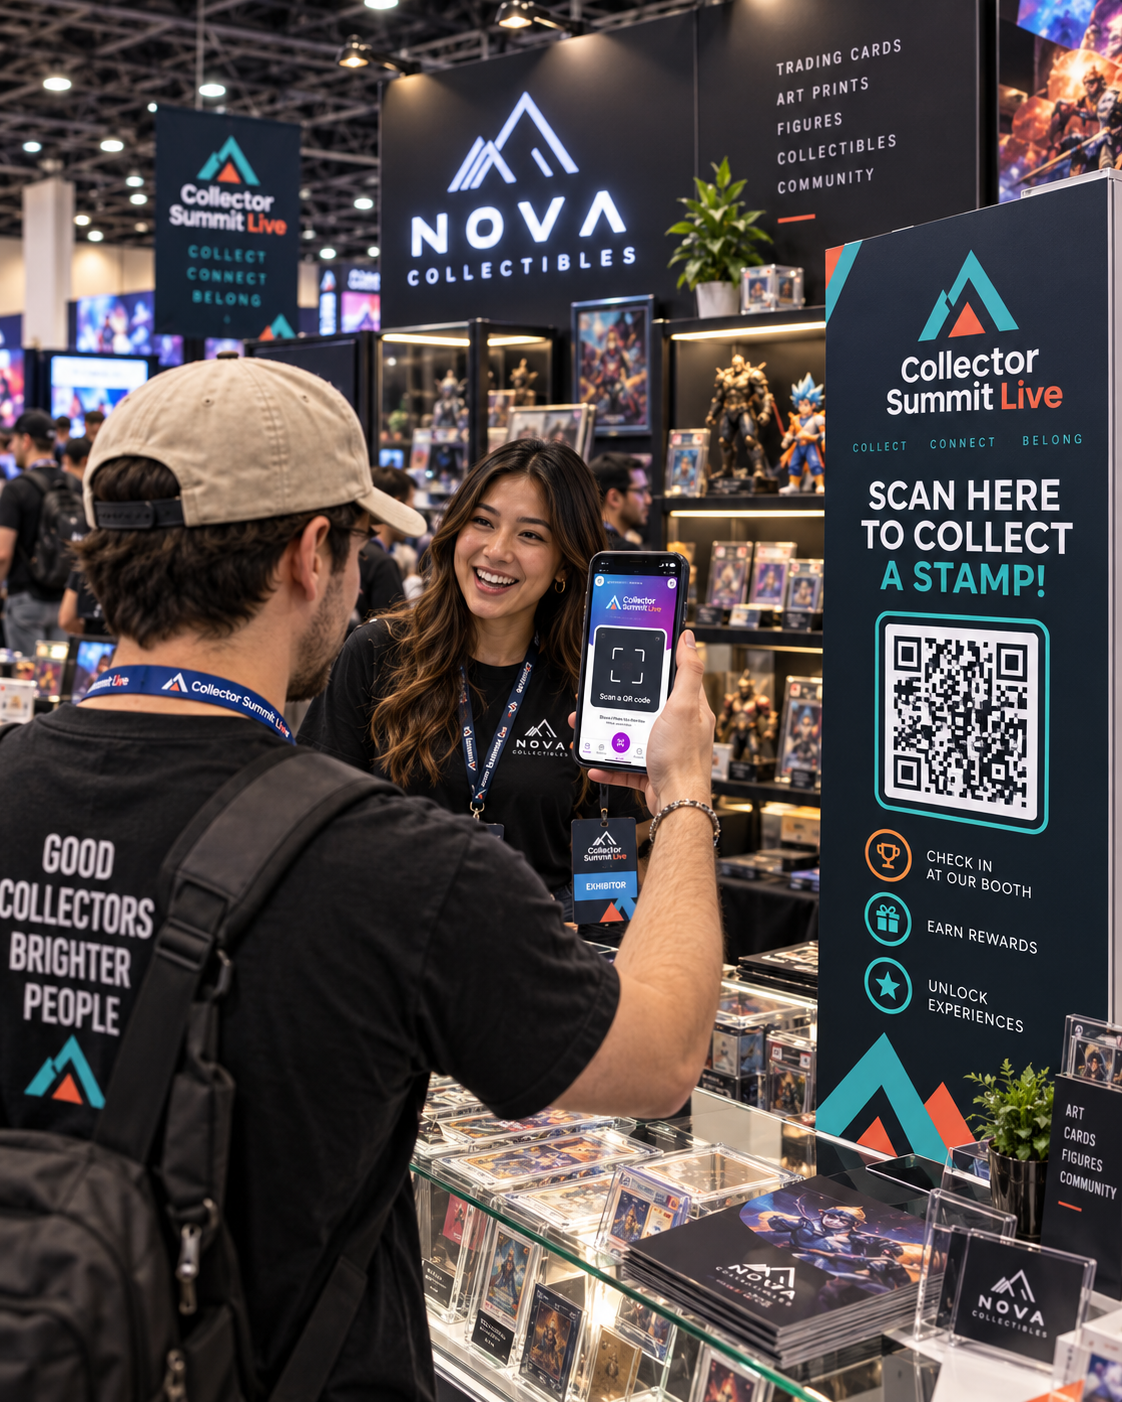
StampRise is a browser-based digital event passport and gamification platform built for trade shows, conferences, festivals, and brand activations. Attendees scan QR codes at booths and stations to collect stamps, earn rewards, and climb leaderboards. The platform serves event organisers across seven regions, including the EU, UK, Singapore, South Africa, UAE, United States, and Australia, with clients including the Singapore Fintech Festival 2026 and an active enterprise pipeline across multiple continents.
The challenge
Multi-framework compliance across seven regions without a security or compliance team
StampRise operates a multi-region platform that requires handling the personal data of many different attendees, which meant SOC 2, ISO 27001, and GDPR were required for many enterprise contracts. There was too much to do and too little time: StampRise needed compliance across all three frameworks simultaneously, and needed to achieve it without a dedicated security function, all while Founder & CEO Qutayba Al-Eesa was focusing on selling, shipping, and onboarding.
What StampRise tried first: StampRise needed SOC 2, ISO 27001, and GDPR simultaneously and across seven regions. At a prior company, Al-Eesa had attempted ISO 27001 compliance through consultants, manual documentation, and manual evidence collection. Three months into repeating this strategy at StampRise, the effort stalled with no audit readiness in sight, and the team decided to try a different plan.
StampRise’s pivot point: The StampRise team scoped the traditional route: A consultant would have cost five figures, taken weeks to finish, and still left Al-Eesa to collect evidence manually with no support for ongoing monitoring. The complexity of this work was only going to grow, with the company already having to reconcile three overlapping frameworks across seven regulatory environments to support controls that needed to keep up with live events involving thousands of attendees.
Why StampRise chose Vanta: Vanta stood out from options that merely provided point-in-time snapshots. It unified all three frameworks under a single control set, automated evidence collection, and connected natively to StampRise's existing stack–all continuously, not just at audit time. Native integrations with Google Workspace, GitHub, Cloudflare, and StampRise's existing stack removed friction, and Vanta's policy library offered usable foundations rather than generic boilerplate. Finally, with the support of Vanta's auditor ecosystem, StampRise could eliminate the guesswork of finding qualified partners for attestation and penetration testing.
{{quote-2}}
The Vanta impact
Building a continuously monitored, multi-framework compliance program
StampRise used Vanta to build a unified control set across SOC 2, ISO 27001, and GDPR, allowing them to replace three sequential projects with a single, continuously monitored compliance program. "Evidence collection is continuous rather than a scramble before an audit,” says Al-Eesa. “Access reviews, device compliance, vendor assessments, personnel onboarding, and policy acceptance are all tracked as they happen. I do not maintain a spreadsheet of who approved which policy on which date, because the platform already knows."
Here’s how StampRise deployed Vanta:
StampRise is on track for full attestation across all three frameworks by the end of Q4 2026, and has assembled many supporting documents, including policy sets, ROPA, DPIA, DPA, vulnerability reports, access records, and internal audit programme. This compliance posture positions it ahead of larger competitors and opens enterprise deals that would previously have been out of reach for a small team.
{{quote-3}}