Prove your AI agents are truly safe
Cover the unique risks traditional audits miss. With Agentic Trust Controls, effortlessly extend your current compliance program, put evidence collection on autopilot, and assure buyers your agents are safe.
The Agentic Trust Platform powering security for over [customer_count] customers


Easily catch what standard audits miss
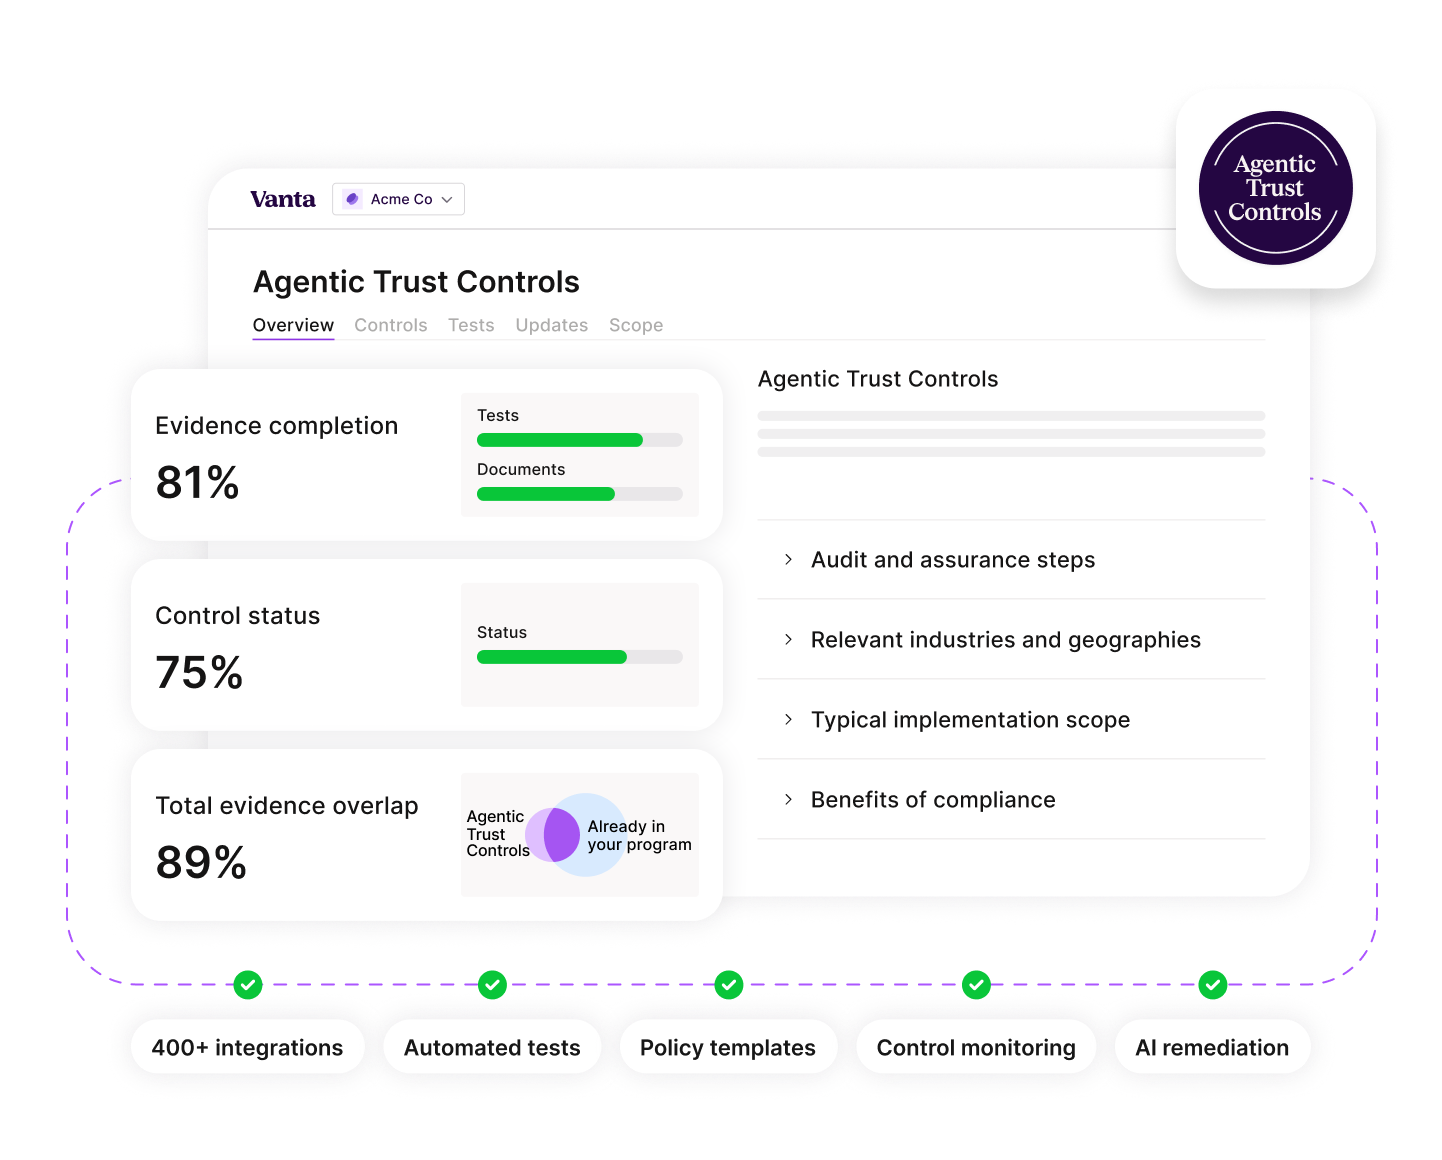
Effortlessly extend your compliance program with controls, policies, and tests for agent identity, tool use, memory, delegation, and more—risks traditional compliance leaves exposed.
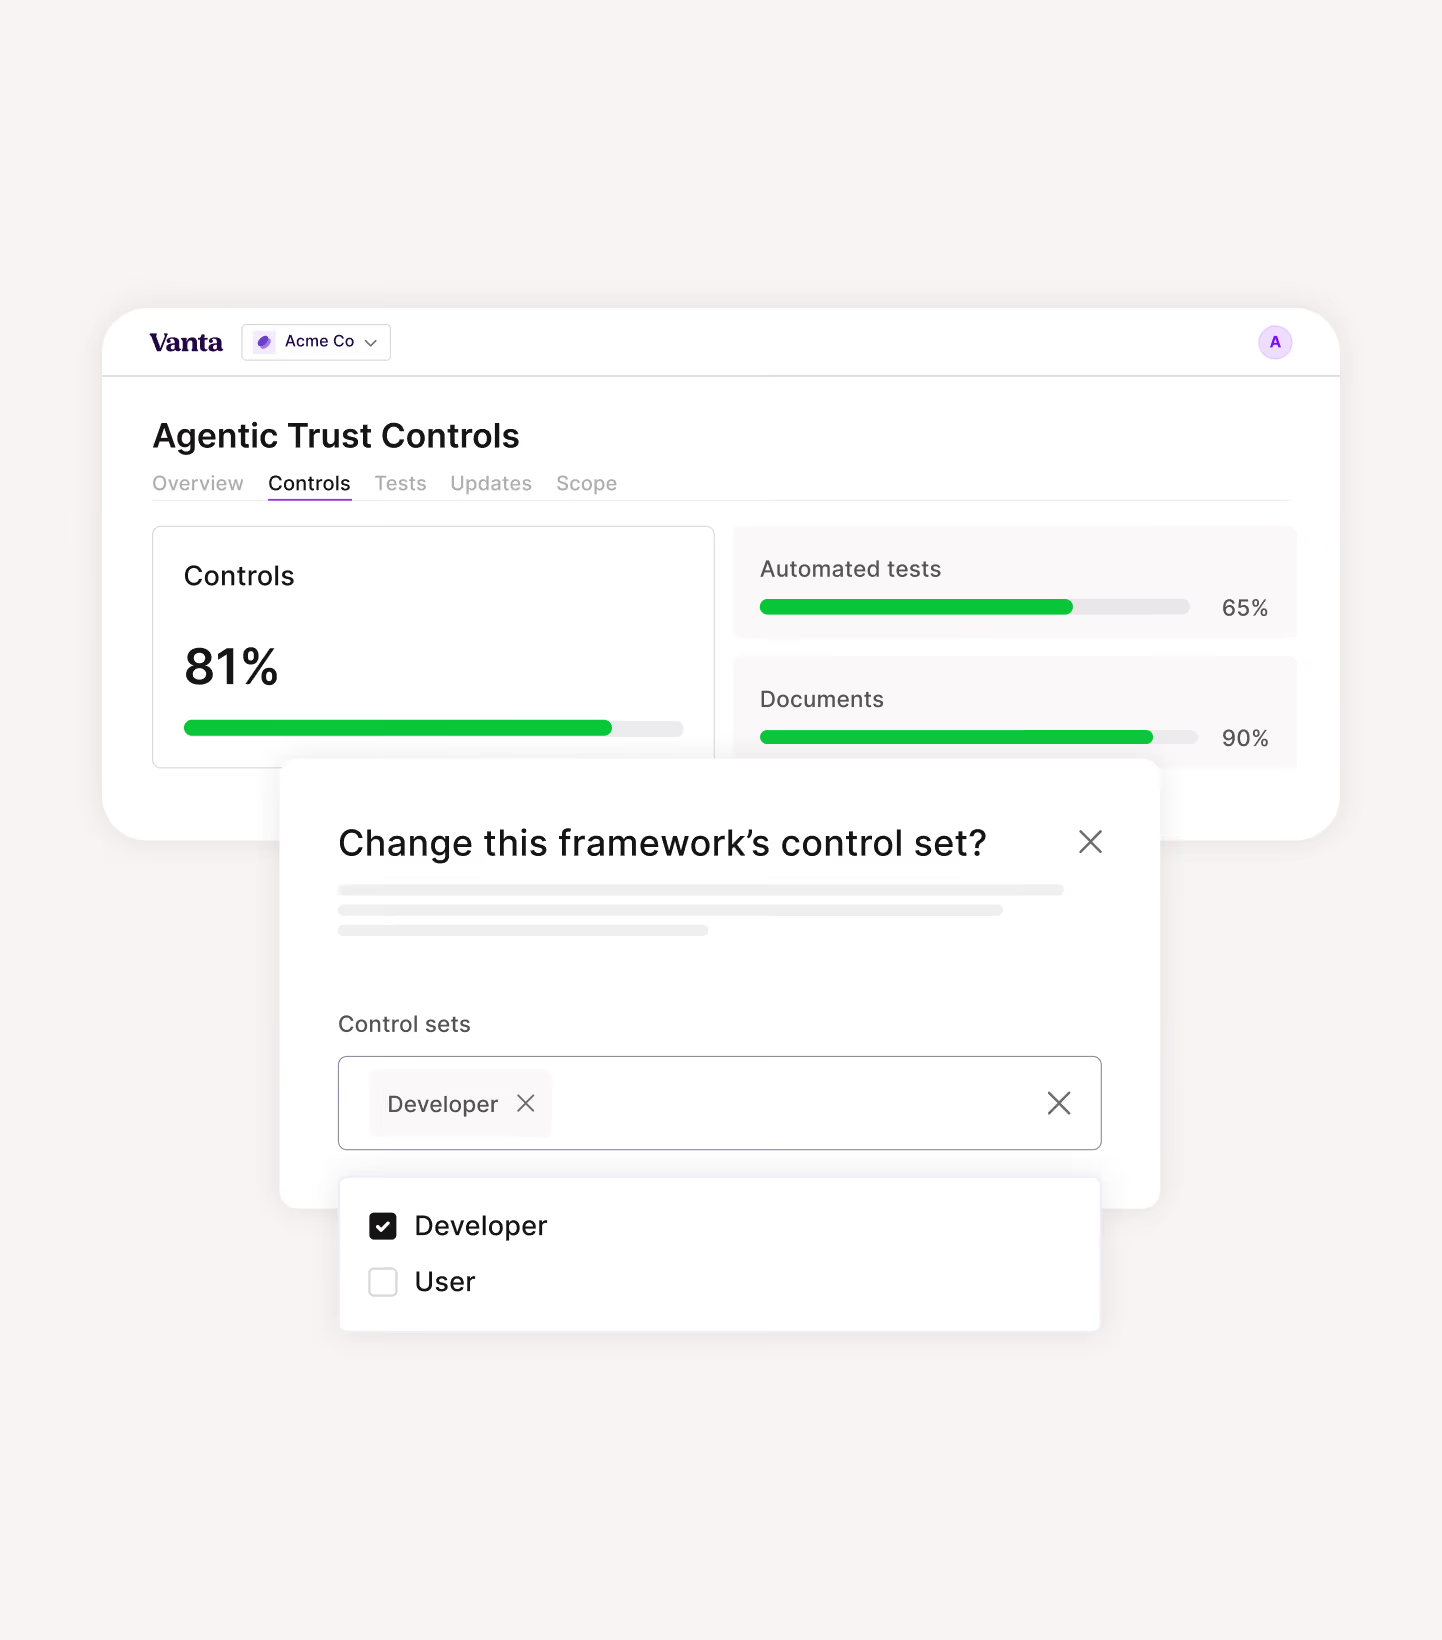
Adapt controls to how you actually work
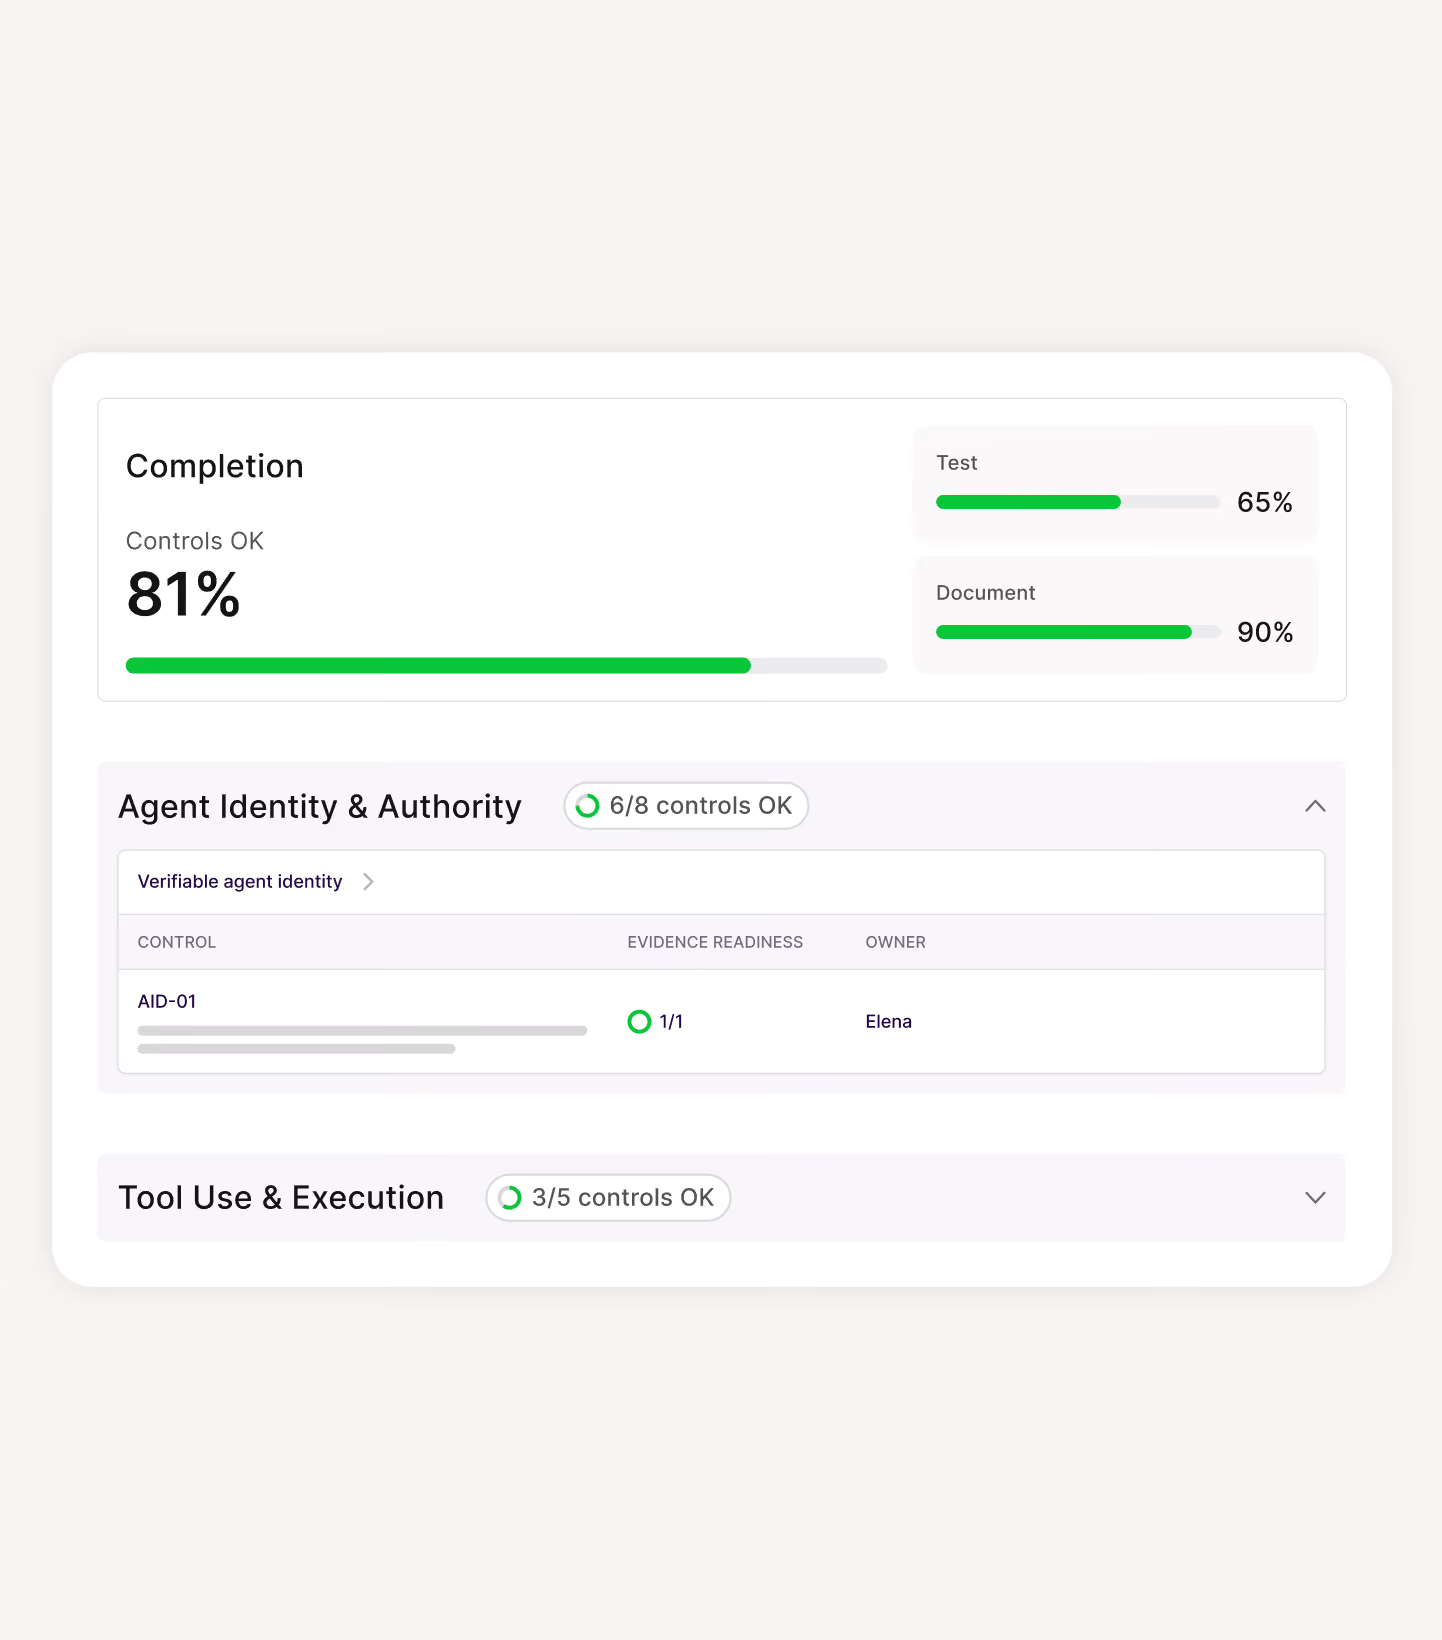
Secure your agents without changing how you work. Pick a developer baseline for built agents, a user baseline for deployed agents, or both—with role-specific controls spanning identity, guardrails, vendors, and training.
Automate compliance from day one
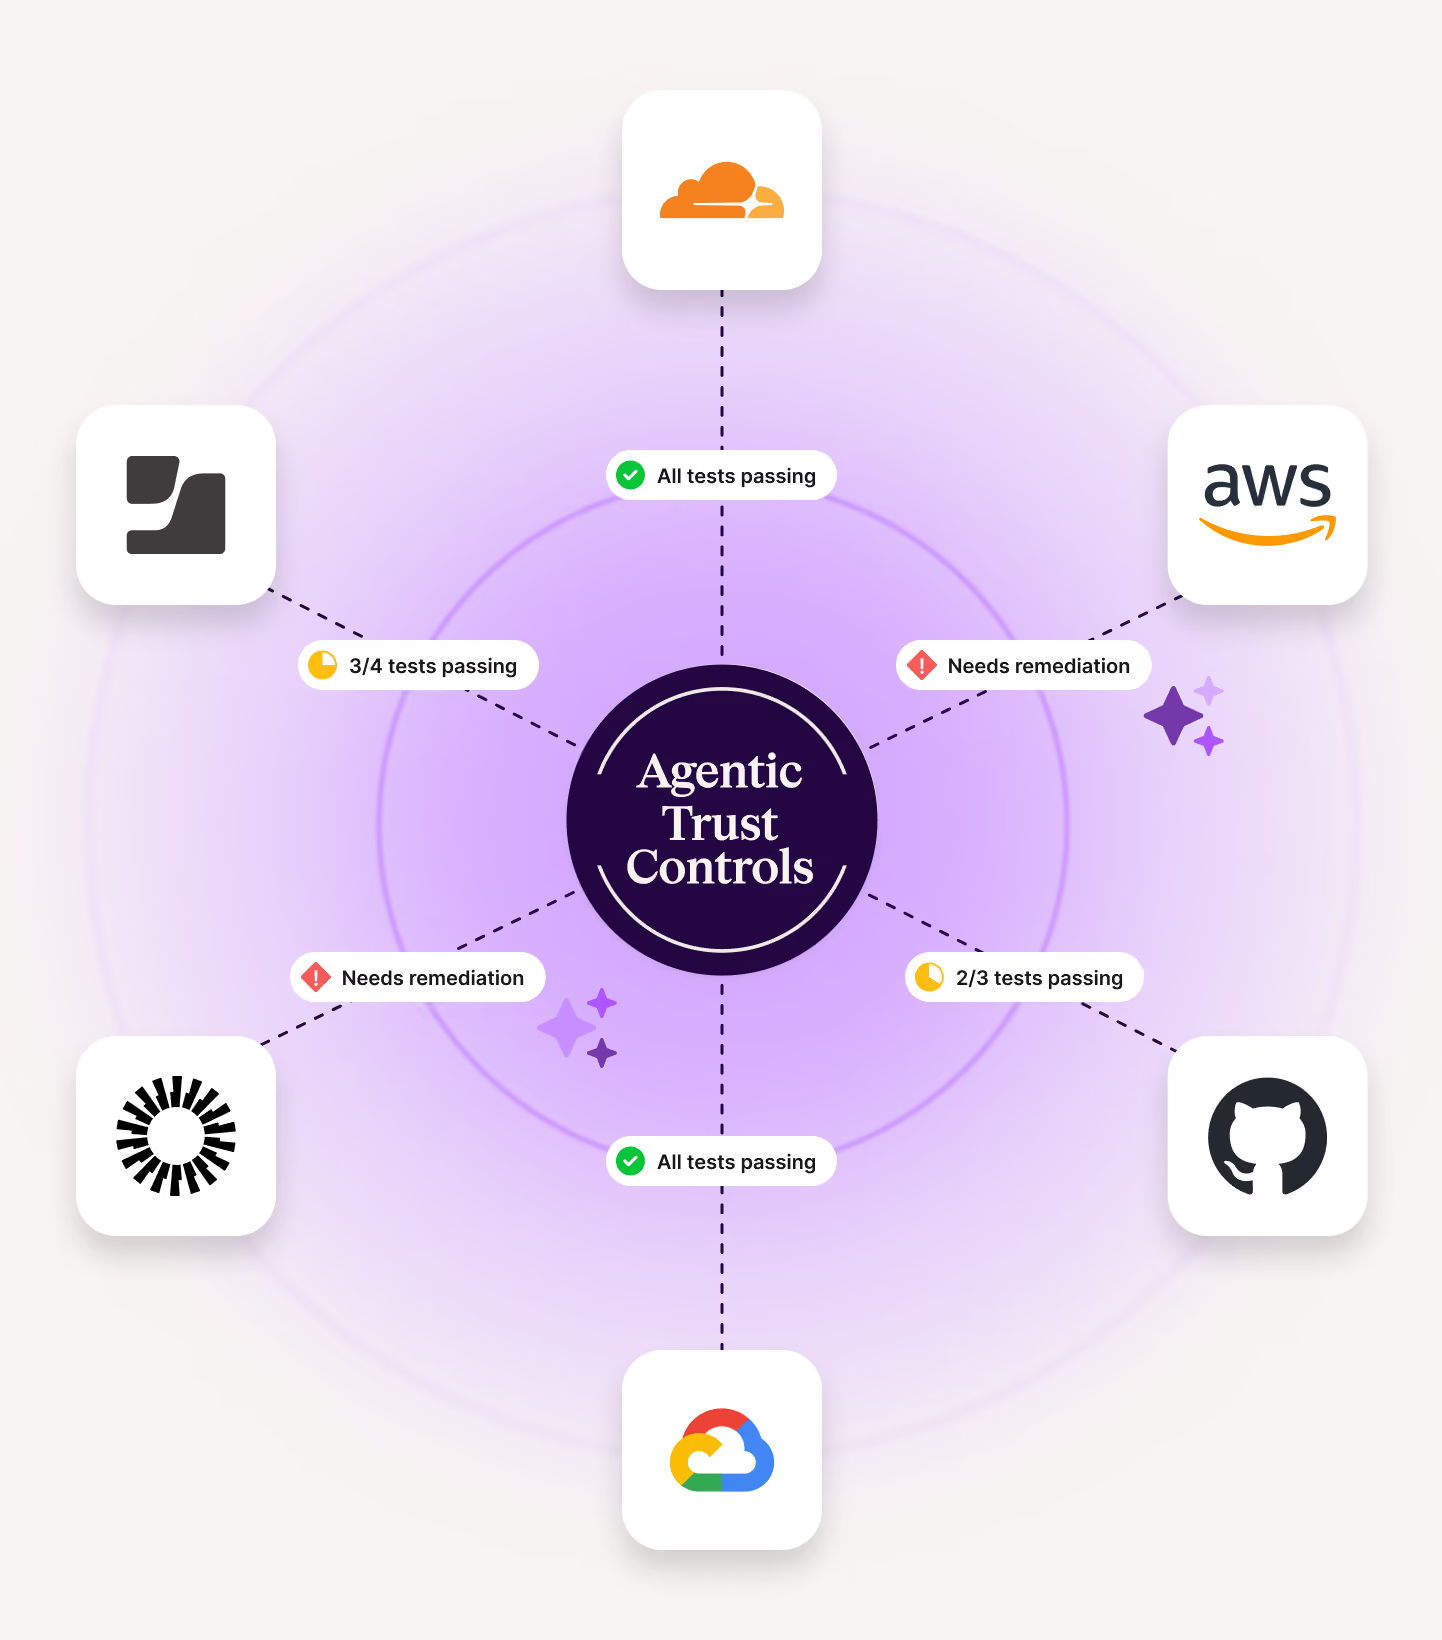
Stay continuously compliant without the manual work. Vanta runs [tests_count] automated tests to review evidence, flag gaps, and suggest fixes, integrating with [integrations_count] tools, including AI platforms like OpenAI and Anthropic.
Additional features

Centralized control management
Track control ownership, evidence, and status across all 12 risk domains in one place.

Continuous monitoring
Vanta tests your controls automatically and flags gaps as they appear, so you're not re-checking agent posture by hand.

Agent policy management
Draft, update, and maintain agent policies with built-in templates and the Vanta Agent, then track employee acknowledgment automatically.

Risk management
Identify, assess, and reduce agent risk with tailored scenarios, mapped controls, and continuous monitoring across all 12 risk domains.

Trust Center
Share your agent control status, policies, and readiness artifacts with buyers during security reviews.

AI-powered compliance
Use the Vanta Agent to flag evidence gaps, map controls, and speed up remediation across your agent program.


Learn more about Agentic Trust Controls
AI Governance Checklist
Use this 6-step checklist to build a scalable, compliant AI governance program.

The EU AI Act Checklist
Get our free checklist to understand what’s required under the EU’s AI Act, how ISO 42001 fits in, and how compliance builds trust—and a competitive advantage.

ISO 42001 Compliance Checklist
The ISO 42001 compliance checklist helps to lay the foundation for what your organization should expect when working towards certification.
FAQ
Agentic Trust Controls (ATC) are a control set for agentic AI risk: 65 controls across 12 domains, delivered as two baselines. They map to ISO 27001, ISO 42001, AIUC-1, CSA AICM, MITRE ATLAS, NIST AI RMF, and OWASP Top 10. Agentic Trust Controls started as an open source project with over 350 contributors in its first month. Now, we've built these controls into Vanta and introduced it as a framework.
The 12 domains cover agent identity and authority (AID), tool use and action execution (TUE), reasoning and instruction integrity (RII), memory and state integrity (MEM), multi-agent systems and delegation (MAS), human oversight under autonomy (HOA), runtime behavioral monitoring (RBM), supply chain and component provenance (SCP), adversarial robustness and testing (ADV), output integrity and anti-fabrication (OUT), resource and cost abuse (RES), and agentic governance and accountability (GOV).
AIUC-1 is a standalone auditable standard. The CSA AI Controls Matrix is broader, covering AI systems generally. OWASP offers technical guidance rather than an audit-ready baseline. ATC layers agent-specific controls onto frameworks you already hold.
You declare the ATC controls in scope for your next ISO 27001 or ISO 42001 audit. Because they sit inside a framework your auditor already assesses, the same audit produces third-party evidence for them.
Both. Agentic Trust Controls is a standalone framework, and the controls also layer onto your existing ISO 27001 or ISO 42001 categories, so there is no separate control set to manage. The same baseline can map to different frameworks, so you are not locked in.
Get compliant and build trust—fast