Vanta AI Governance
BlogProduct updates
November 12, 2026

Govern AI at machine speed

Written by
No items found.
Reviewed by
No items found.

Accelerating security solutions for small businesses 
‍

Tagore offers strategic services to small businesses. 

A partnership that can scale 
‍

Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate.

Standing out from competitors
‍

Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

AI adoption is accelerating, and so is the need to govern it. Employees are adopting new tools, developers are building agents, and those agents are gaining access to sensitive data and the ability to act across business systems. As adoption accelerates, businesses need to know what AI is running, what it can do, and whether it’s operating within the boundaries they’ve set.

‍

That takes more than an inventory or a written policy. It requires an ongoing connection between the rules a business sets and how AI behaves—testing for vulnerabilities, monitoring activity, and intervening when boundaries are crossed. Every step should build confidence and evidence that safeguards are working.

‍

That’s why Vanta has signed a definitive agreement to acquire Pillar Security, a leading runtime security platform. Together, we are building the definitive system of runtime action for AI governance—connecting policies to the technology that tests, monitors, and enforces them in practice. By bringing governance and runtime protection together, we’ll help businesses adopt AI with confidence, prevent harm, and continuously demonstrate how they manage AI risk.

‍

AI governance, connected to your business

Vanta’s vision is to help you govern AI as fast as you adopt it—connecting how you discover, control, and test AI with the compliance program you already manage.

‍

The foundation is Vanta’s Trust Graph. By connecting AI tools and agents to owners, vendors, systems, data, risks, and controls, it provides the context to understand what matters. An agent accessing sensitive customer data deserves different scrutiny than a tool summarizing public information. Those relationships help teams prioritize risk and decide what to do next.

‍

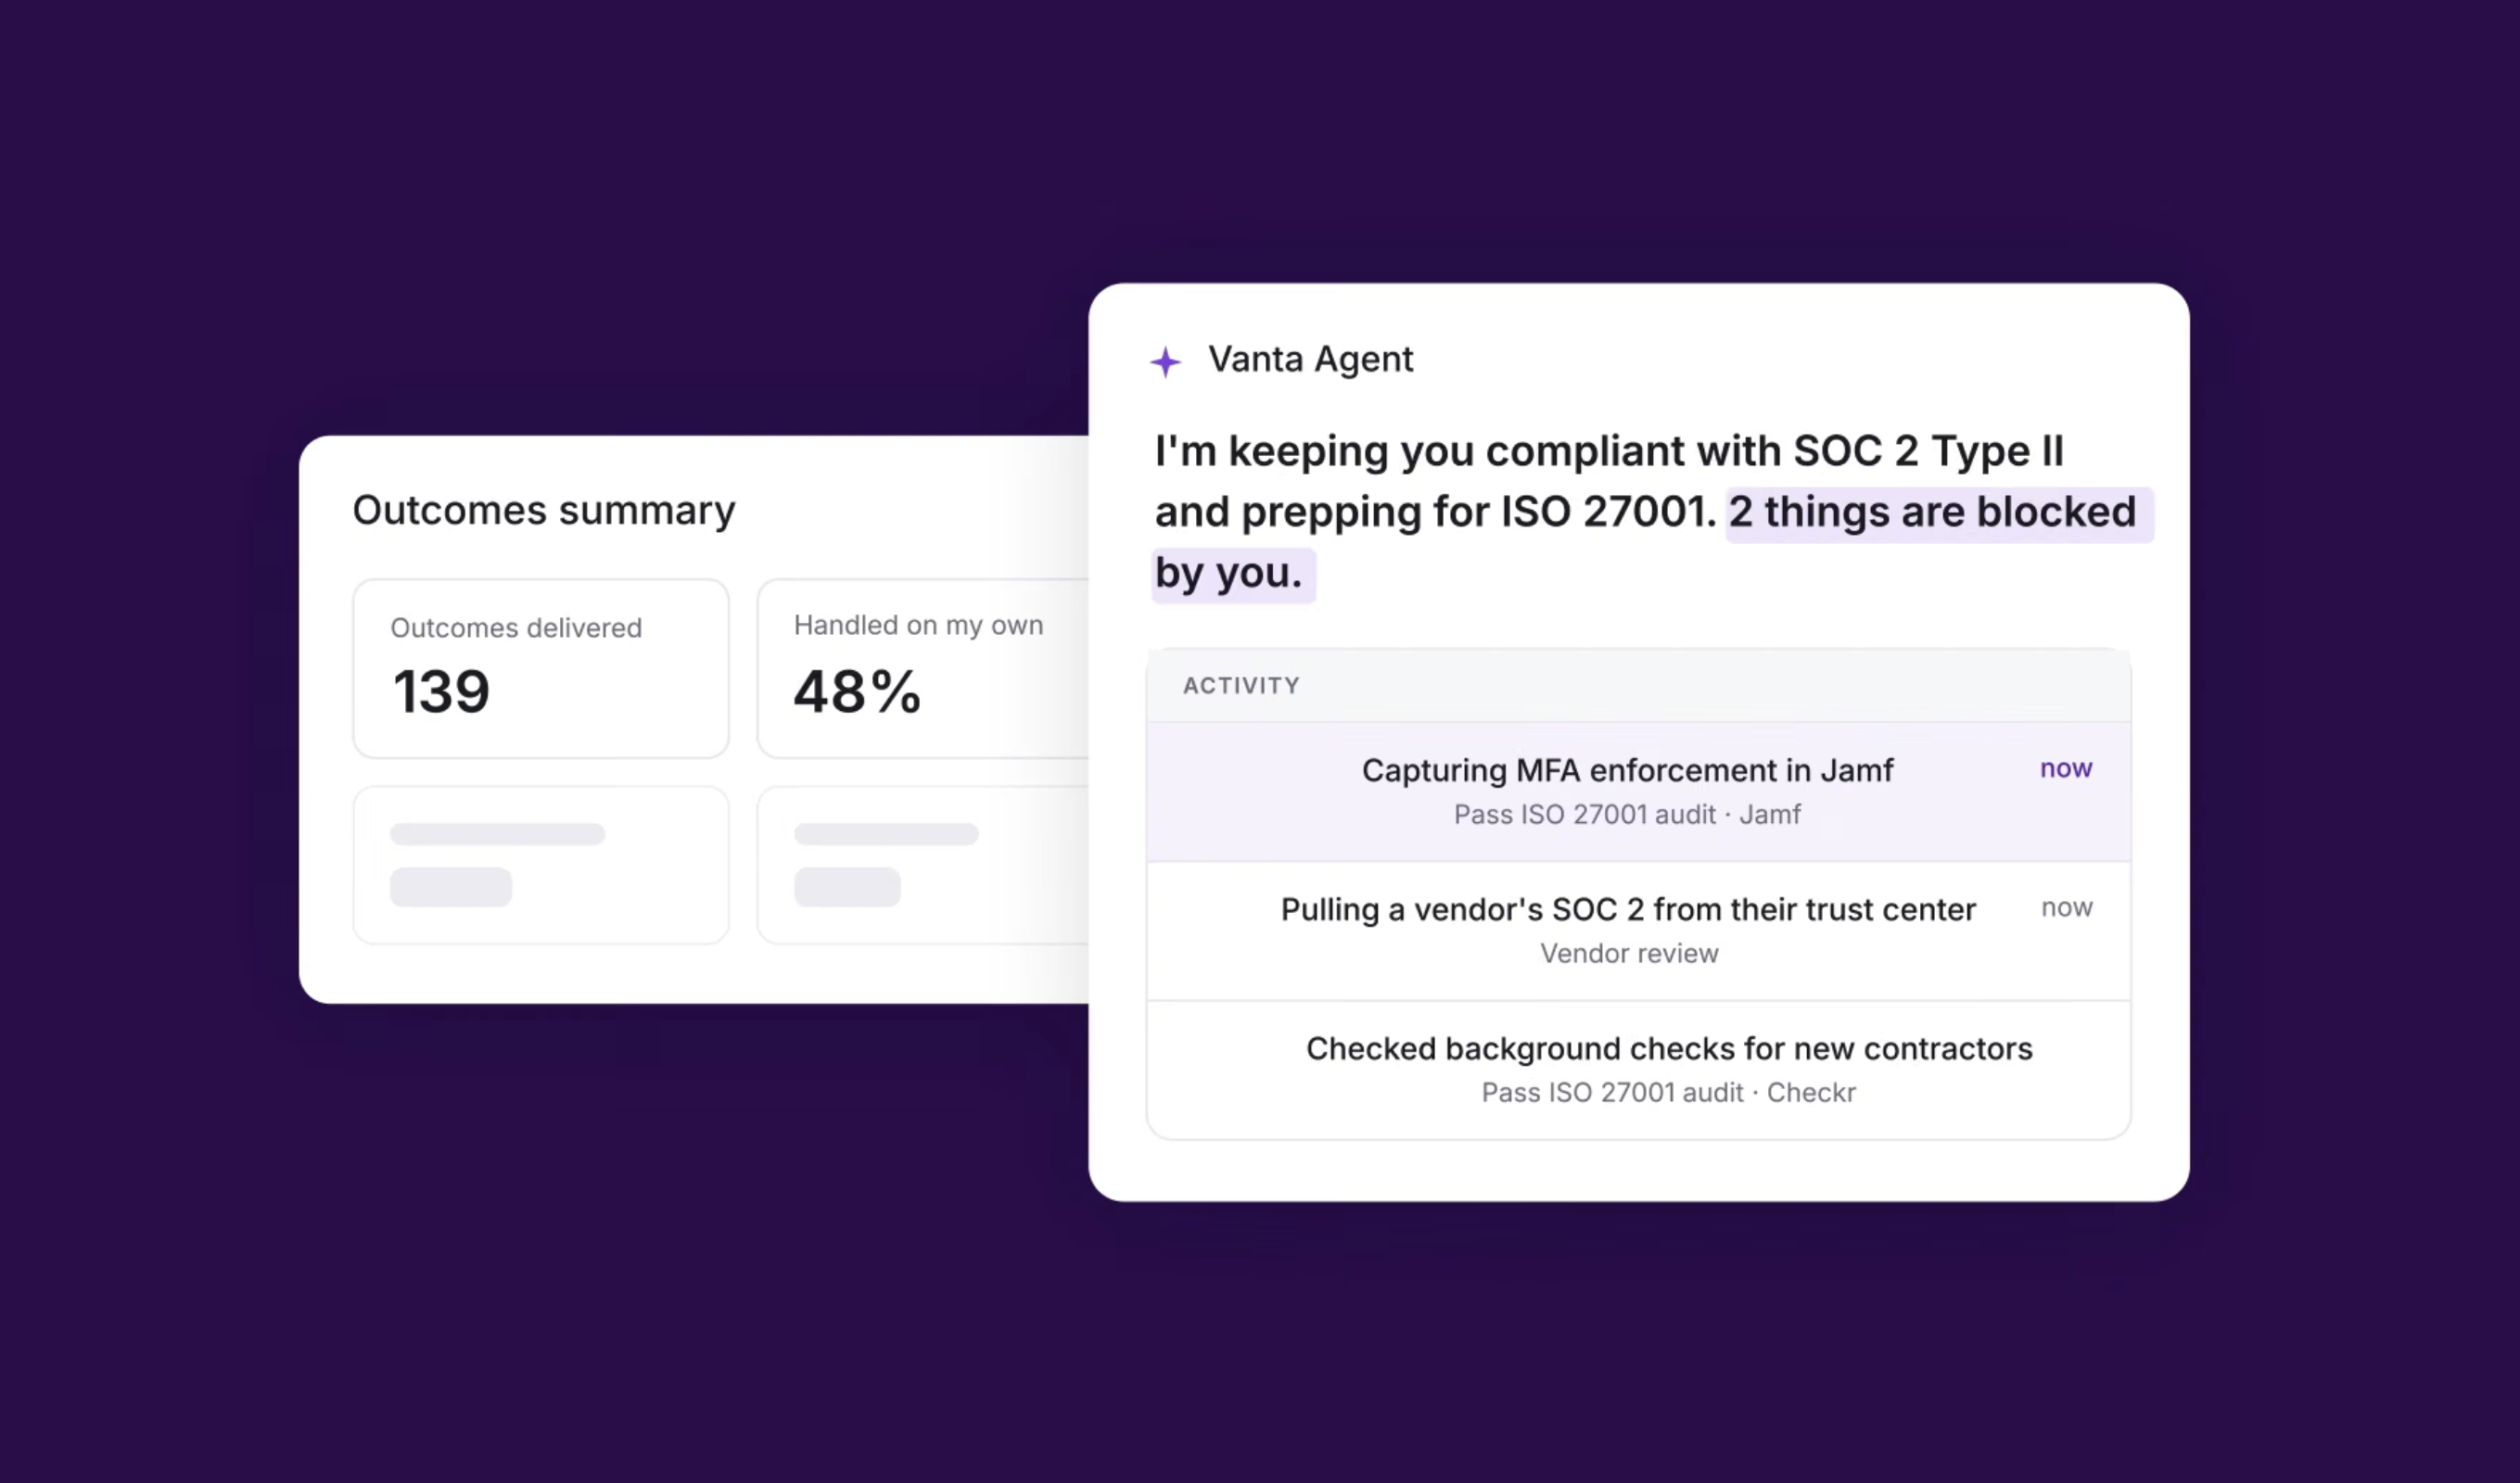
The Vanta Agent helps move that work forward: recommending next steps, flagging issues that need attention, and keeping evidence and documentation current. Our vision extends that assistance into coordinated action, helping teams investigate findings and initiate remediation.

‍

“On our first day in Vanta’s AI governance early access program, we discovered an AI app we didn’t know was being used. The inventory was simple and effective, it's exactly what we’d been looking for to understand the AI in our business and start managing that risk.”
— Roze San Nicolas, MergeWorld

‍

Bringing Pillar’s AI security expertise and technology into Vanta will extend this approach into adversarial testing and runtime protection. Together, we’re building toward end-to-end security for the entire agent lifecycle, grounded in four connected pillars:

‍

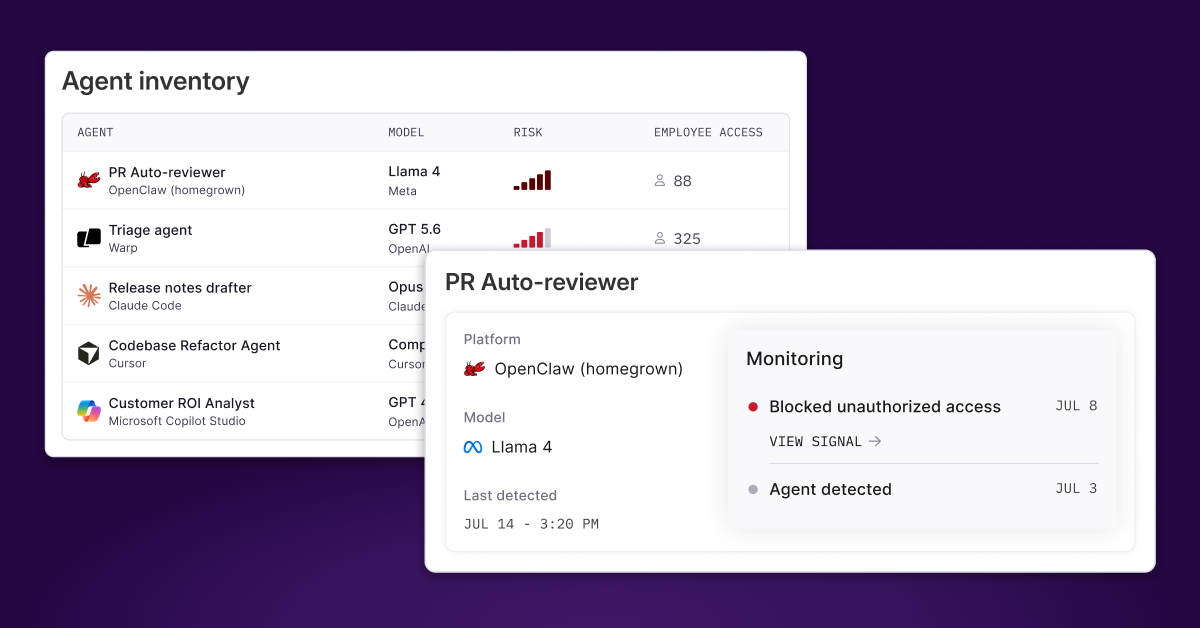
  • Discover: Understand your AI and its risk. Build a connected view of the AI tools, agents, models, and MCP servers across your business. Understand who owns them, how they’re used, and what they can access. Connect that inventory to approved use cases and impact assessments so you can identify gaps, establish accountability, and focus on the AI that presents the greatest risk. Inventory will be available in January. 
  • Control: Turn policy into boundaries. Define how AI should operate, then connect those expectations to its behavior. Our vision includes monitoring for suspicious activity, guardrail violations, and deviations from approved use cases, alongside runtime enforcement to stop disallowed actions. Give teams the context to investigate and respond when behavior crosses a boundary. Guardrails will be available in 2027. 
  • Test: Find weaknesses before they become incidents. Policies and guardrails need to hold up under real conditions. With Pillar’s adversarial testing capabilities, we plan to help teams uncover exploitable paths and evaluate whether safeguards work as intended. Connect findings to business context so teams can prioritize remediation and strengthen defenses as agents evolve. Red teaming will be available in 2027. 
  • Prove: Make governance part of continuous compliance. Connect inventory, assessments, testing, guardrail activity, and remediation to your controls and compliance program. Build an ongoing record of how you identify and manage AI risk, supporting alignment with frameworks such as ISO 42001 and NIST AI RMF. Every assessment completed, safeguard tested, and issue resolved should contribute to that proof. With Vanta, our goal is to make demonstrating trust a continuous outcome of governing AI—so your business can adopt it with confidence.

‍

AI Governance by Vanta will be available as a paid offering starting in January. 
‍

Access Review Stage Content / Functionality
Across all stages
  • Easily create and save a new access review at a point in time
  • View detailed audit evidence of historical access reviews
Setup access review procedures
  • Define a global access review procedure that stakeholders can follow, ensuring consistency and mitigation of human error in reviews
  • Set your access review frequency (monthly, quarterly, etc.) and working period/deadlines
Consolidate account access data from systems
  • Integrate systems using dozens of pre-built integrations, or “connectors”. System account and HRIS data is pulled into Vanta.
  • Upcoming integrations include Zoom and Intercom (account access), and Personio (HRIS)
  • Upload access files from non-integrated systems
  • View and select systems in-scope for the review
Review, approve, and deny user access
  • Select the appropriate systems reviewer and due date
  • Get automatic notifications and reminders to systems reviewer of deadlines
  • Automatic flagging of “risky” employee accounts that have been terminated or switched departments
  • Intuitive interface to see all accounts with access, account accept/deny buttons, and notes section
  • Track progress of individual systems access reviews and see accounts that need to be removed or have access modified
  • Bulk sort, filter, and alter accounts based on account roles and employee title
Assign remediation tasks to system owners
  • Built-in remediation workflow for reviewers to request access changes and for admin to view and manage requests
  • Optional task tracker integration to create tickets for any access changes and provide visibility to the status of tickets and remediation
Verify changes to access
  • Focused view of accounts flagged for access changes for easy tracking and management
  • Automated evidence of remediation completion displayed for integrated systems
  • Manual evidence of remediation can be uploaded for non-integrated systems
Report and re-evaluate results
  • Auditor can log into Vanta to see history of all completed access reviews
  • Internals can see status of reviews in progress and also historical review detail
FEATURED VANTA RESOURCE

The ultimate guide to scaling your compliance program

Learn how to scale, manage, and optimize alongside your business goals.