Curated content for the trust management expert. Get the latest on security trends, compliance frameworks, and Vanta news.
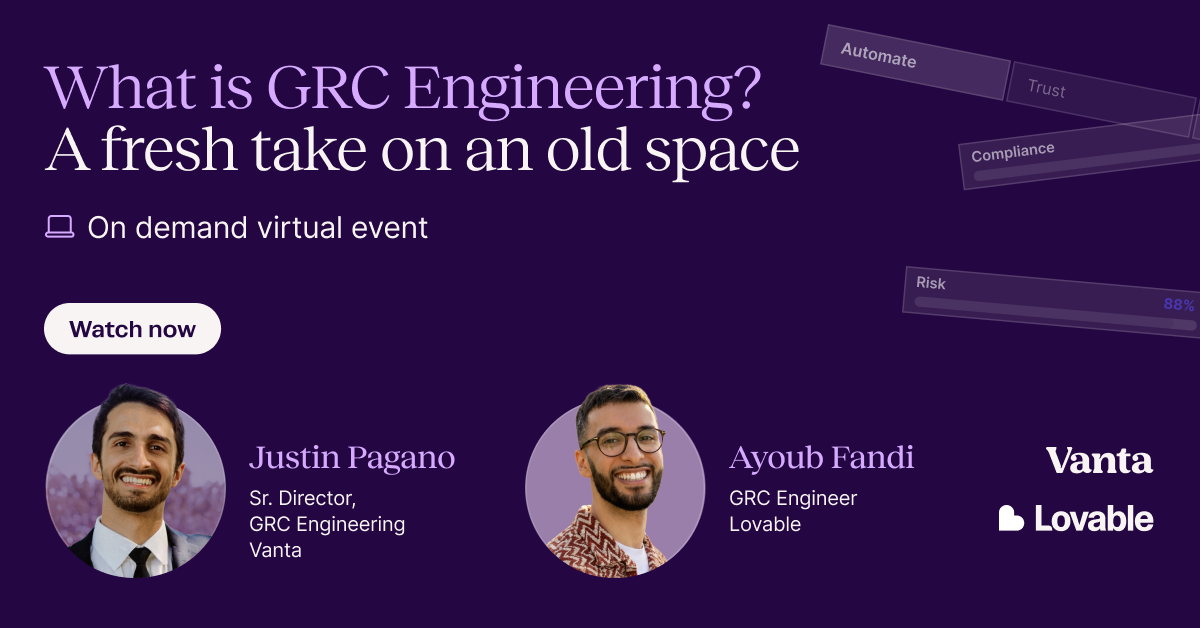
Watch on-demand to hear from Lovable and Vanta and learn what modern GRC actually looks like when it is done right.
How Vanta Government Cloud achieved FedRAMP 20x Moderate, with key lessons.
For years, security teams proved trust once a year during audits, and their customers accepted static PDFs. That era is over.
Our latest Trust Signals drop explores how builder culture is changing the risk landscape, and what happens when security is still built for a world where only product engineers shipped.
Get the latest news and resources in your inbox. Sign up for our newsletter!
In this post, we'll cover the scope and applicability of Germany's IT Security Act 2.0, as well as the new definitions and audit and security requirements for both critical infrastructure operators and digital service providers.
Partnership with Vanta delivers more certifications, happier customers, and business growth for Kobalt.io.
Learn how GDPR and ISO 27001 compliance overlap and how each standard provides more overall security for your organization together than they do individually.
Building and security startups is hard. But, it doesn't have to be. Learn the six tips that will not only improve your security, but will make it easier for your team to scale quickly and safely.
What are the costs involved with becoming ISO 27001 certified? We break down all the possible ways that the cost of ISO 27001 certification can add up and share how to minimize expenses.
Not all security monitoring platforms are created equal. Use these five tips to help decipher which questions to ask in order to determine the right automated security platform for your organization.
Learn the ins and outs of ISO 27001 compliance for startups and get a better understanding of why compliance helps improve your security posture.
What’s the difference between a SOC 1 and SOC 2 report and which one does your business need? Learn the details of each to understand which report makes sense for your organization.
Noticing a lot of similarities between CCPA vs. GDPR? Find out what the differences are between these two regulations and if you’ll need both.
Creating a continuous security process within your organization can be complex, especially if you lack time and budget. Learn how to create continuous security without a security team.
Get a step-by-step breakdown of the SOC 2 compliance guidelines in this checklist.